Compliancy Group vs 5 Alternatives: HIPAA and OSHA Compliance Tools for Small Medical Practices
ExpiryEdge is our first pick for a small practice that already has policies and a risk analysis, and keeps missing the follow-through. It keeps every date around the program from slipping: the annual risk review, each vendor's BAA, each nurse's bloodborne pathogens refresher. For the policy library, risk questionnaire and training courses, pair it with Compliancy Group: one login gives you policy templates, risk work, staff training, BAA tracking and an OSHA program with a templated exposure control plan.
Accountable is the pick if you want to see a price for a program before you talk to anyone. Abyde and HIPAA One suit practices that want guided risk assessments, and Total Medical Compliance suits practices that want a trainer on site.
Before the table, one disclosure. We make ExpiryEdge. What we say about Compliancy Group and the other four comes from their own sites and help pages, read on 7 November 2026, and every claim links back to the page it came from.
| Tool | Collects signed BAAs from vendors | Reminds each staff member before training lapses (email, SMS, WhatsApp) | Escalates overdue items to the practice manager | Annual reviews run as recurring checklists | Policies, risk assessment and courses | Published pricing / free trial |
|---|---|---|---|---|---|---|
| ExpiryEdge Top pick | Yes, no-login link with e-signature | Yes, email, SMS, WhatsApp, Slack, Teams | Yes, automatic | Yes, assigned steps with a log | Pair with a program or the free HHS SRA Tool | $29-$199/month, 14-day free trial |
| Compliancy Group | Send, sign and store | Schedules and tracks OSHA training | Not stated | Tracks the annual ECP review | Yes, templates, risk tools, training | Not published |
| Accountable | Sends and tracks BAAs | Training completion tracking | Not stated | Not stated | Yes, AI-powered SRA, templates, training | $199-$799/month, 7-day free trial |
| Abyde | E-sign, alerts before expiry | Training videos and quizzes | Not stated | Not stated | Yes, tailored SRA, policies, OSHA | Not published |
| HIPAA One | Templates, e-signatures, deadline reminders | On-demand training | Not stated | Not stated | Yes, automated SRA, policy library | Not published |
| Total Medical Compliance | Not stated | On-site and online training | Not stated | Not stated | Training and risk analysis services | Not published, quote form |
How we compared these tools
A small practice usually fails an audit on a date: an unsigned BAA, a refresher a year overdue, a review nobody ran. So our columns ask how each tool collects BAAs, reminds staff, escalates and runs the yearly reviews. One column covers the program itself (policies, risk assessment, courses), because a practice without one needs it, and the last shows the price. Where a vendor's pages don't say, the table says "Not stated". We read each vendor's own product, pricing and help pages on 7 November 2026 and checked the rules against eCFR, HHS, OCR and OSHA. We didn't buy a paid trial of every program. ExpiryEdge is our product, so read what we say about it knowing that.
The paperwork an OCR or OSHA visit asks for
Start with the risk analysis. The HIPAA Security Rule, at 45 CFR 164.308, requires an "accurate and thorough assessment" of the risks to electronic health information. It doesn't say how often. HHS guidance on risk analysis calls it an ongoing process and gives annual, or as needed, as an example, plus a fresh look after an incident, a new system or key staff leaving.
Regulators do check. In April 2025, OCR settled with Comprehensive Neurology, a small New York neurology practice, for $25,000 after a ransomware attack. It was the eighth action in OCR's Risk Analysis Initiative.
Then keep the paper. 45 CFR 164.316 says you keep Security Rule documentation for 6 years from when it was created or last in effect, whichever is later. Your 2026 risk analysis needs to be findable in 2032.
Vendors who touch patient data need a business associate agreement before they start. HHS's sample BAA provisions list what it must cover, including return or destruction of data when the contract ends. Your IT firm, billing company, shredding service and cloud phone system probably all qualify.
OSHA adds its own calendar. Under the bloodborne pathogens standard, you review your exposure control plan at least annually, and staff with exposure get training when they start and again within one year of their last session.
- HIPAA risk analysis reviewed, and redone after any new system or incident
- Policies reviewed and staff sign-off collected
- HIPAA training for every workforce member
- Bloodborne pathogens training within 12 months of each person's last one
- Exposure control plan reviewed and updated
- Every vendor BAA signed, filed and checked at renewal
- Documentation kept for 6 years
Do you need a program, or just the follow-through?
Answer one question first: do you have a program, or do you need one? If you don't have current policies and a documented risk analysis, buy a program. Compliancy Group and Abyde cover HIPAA and OSHA together, and Accountable shows its price up front.
If you do have a program, list every recurring date it creates and who owns each. If that list lives in someone's head, a tracker is the cheaper fix. Test any tool by setting up one vendor BAA and one staff member's training, then check who gets reminded and when.
See our medical practice compliance software guide for the full picture, the payer enrollment and credentialing comparison for provider dates, and our OSHA training tracker for the training side. The common healthcare compliance gaps post covers what usually slips.
1. ExpiryEdge: best for keeping every BAA, review and training date around your program current
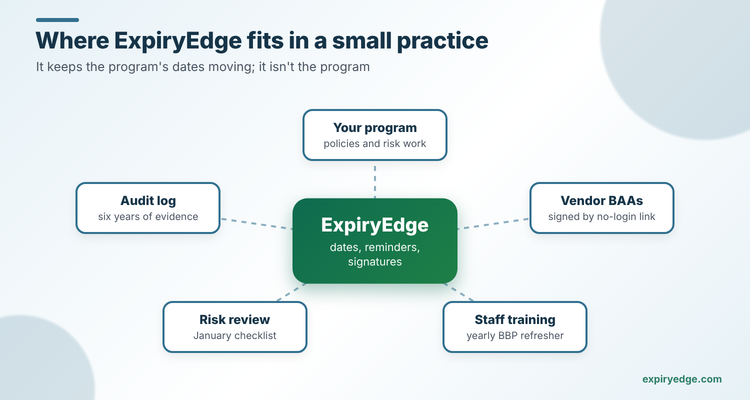
With ExpiryEdge, the gaps an auditor finds first, an unsigned BAA or a refresher a year overdue, stop happening. The practice manager no longer chases vendors and staff by memory, and the evidence for each date is one export away.
Put each vendor in as a record with its BAA attached. Send a new vendor a request link they open without a login: they sign the BAA with a legally binding e-signature, upload their security summary and add their contact details. Your reviewer approves or rejects each item with a comment, and a rejected item reopens on the same link. When the vendor contract renews, ExpiryEdge reminds you to check the BAA still fits.
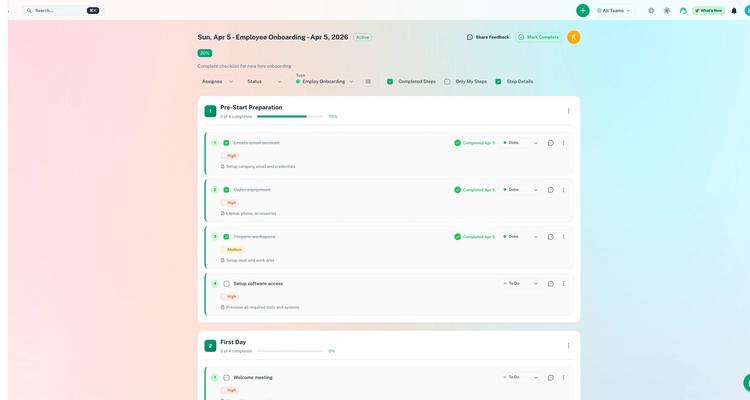
Staff get records too. Maria, a medical assistant, gets a WhatsApp message 30 days before her bloodborne pathogens training is a year old, and the practice manager gets an escalation if it's still open on the due date. The annual risk review and the exposure control plan review become scheduled checklists that run every January, with each step assigned and logged. Every action lands in an exportable audit log, which helps when someone asks for six years of evidence.
Try it with your own BAAs in 15 minutes:
- Import a CSV of your vendors with a custom field for the BAA signed date and the contract renewal date.
- Pick your IT firm and send it a no-login request link with an e-signature field for the BAA and a file upload for its security summary.
- Create a recurring January checklist for the risk review and exposure control plan, and assign each step to a named person.
Pricing: $29 a month for one user, rising to $199 for 50 users, with a 14-day free trial and no card needed. You can compare plan limits on the pricing page.
Good to know: ExpiryEdge sits beside the program you already have, whether a consultant's policy binder, Compliancy Group or the free HHS tool mentioned below, and makes sure the dates it creates are met.
2. Compliancy Group: best all-round HIPAA and OSHA program
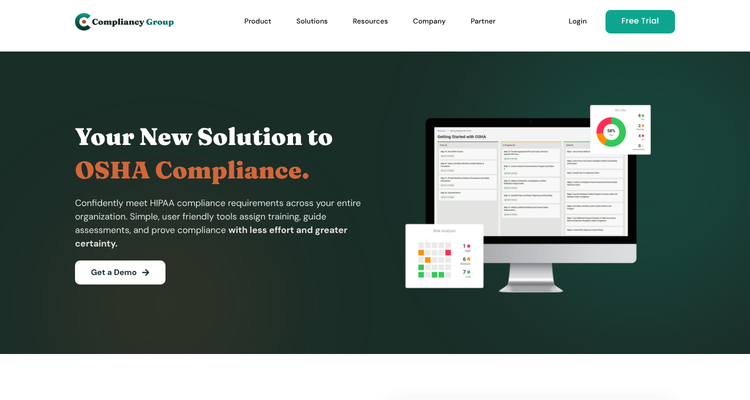
Compliancy Group runs your HIPAA program from one dashboard. Its small practice page lists a Policy Manager with more than 100 ready-to-use templates, risk tools to find and fix issues, and staff training covering HIPAA, OSHA and fraud, waste and abuse. You can send, sign and store business associate agreements in the same place.
The OSHA module is the reason it's our pick for a full program in a medical office. It gives you a templated exposure control plan and tracks the annual review automatically. It schedules and tracks OSHA training, includes a bloodborne pathogens course and organises records such as sharps injury logs. Advisory Services and an AI assistant called Cora answer questions.
Pricing: not published. The pricing page asks you to get in touch, mentions association discounts and offers onboarding packages from self-serve to one-on-one.
Watch out for: there's a free trial button, but the site doesn't say how long it lasts.
3. Accountable: best published price for HIPAA
Accountable is HIPAA software for practices and business associates. Its home page lists an AI-powered security risk assessment with step-by-step remediation, policy templates you publish and assign, annual HIPAA training with completion tracking, and vendor tracking that sends BAAs and stores contracts. The course list includes bloodborne pathogens.
Pricing: published on the pricing page. Basic HIPAA is $199 a month, Plus $299 and Pro $799, each billed monthly, with about 15% off on annual billing. Basic and Plus include 15 employees and Pro includes 20, with extra seats from $9 a month. Every plan has a 7-day free trial.
Watch out for: the home page doesn't mention an OSHA program beyond the bloodborne pathogens course. If OSHA is half your problem, check what's included.
4. Abyde: best guided setup for a practice starting from scratch
Abyde sells HIPAA and OSHA software for healthcare practices. It walks you through a tailored risk assessment, then generates policies, procedures and forms. Staff get training videos, quizzes and your policies in one place, and its OSHA for Healthcare product covers bloodborne pathogens, infectious diseases and workplace violence.
BAAs are signed, sent and received in the cloud, and Abyde notifies you before an agreement expires. You can upload agreements signed elsewhere. Abyde says customers get unlimited access to compliance experts at no extra cost.
Pricing: not shown. The pricing page asks for locations and employees, lists separate SRA, HIPAA and OSHA products, and offers 10% off for paying upfront, but no figures appeared when we checked.
Watch out for: monthly, quarterly and bi-annual billing are all 12-month terms.
5. HIPAA One: best if you want someone to run the risk assessment
HIPAA One, from Intraprise Health, automates the security risk assessment and adds privacy and breach risk assessments. You can import last year's answers and auto-fill what hasn't changed. It includes a policy library, on-demand training and a Business Associate Manager with templates, e-signatures and deadline reminders.
You choose the service level: managed, where Intraprise experts run the assessments, hybrid, or self-service.
Pricing: not published. Intraprise asks you to request a demo.
Watch out for: the product page doesn't mention OSHA, so you'd need another source for the exposure control plan and bloodborne pathogens training.
6. Total Medical Compliance: best for on-site training and audits
Total Medical Compliance is a training and consulting firm rather than a software platform. It runs OSHA and HIPAA training on site or online with CE credit, a HIPAA security risk analysis, on-site facility audits, and monthly OIG, SAM and state exclusion screening. Packages add seats as you hire.
Pricing: not published. You request a custom plan through the quote form.
Watch out for: the site doesn't name a software platform for tracking your program day to day, beyond a training login.
ExpiryEdge as an alternative to Compliancy Group
We put ExpiryEdge first because the gaps an OCR or OSHA visit finds are often dates: an unsigned BAA, a refresher a year overdue. Switch to ExpiryEdge if you already have policies and a risk analysis that a consultant wrote, and what keeps failing is the follow-through. A four-doctor practice with 14 staff and 12 vendors has about 40 dated items a year: training per person, a BAA per vendor, two annual reviews. That fits the $29 Personal plan, or Pro at $49 if three people need logins.
You'd also pick it if your deadlines go well beyond HIPAA. The same records can track the clinic's CLIA certificate, DEA registration and each doctor's licence.
Compliancy Group, or another full program, is still the right call if you've never done a risk analysis, don't have current policies, or want someone to answer "is this a breach?" on a Friday afternoon. Policy wording is the program's job; keeping its dates is ExpiryEdge's.
Frequently asked questions
The Security Rule doesn't set a frequency. HHS calls risk analysis an ongoing process and gives annual, or as needed, as an example. Redo it after a security incident, a new EHR or phone system, or a change in ownership. Most small practices review it once a year.
OSHA's standard requires training when someone starts a job with exposure risk, and again within one year of their last session. You also review the exposure control plan at least once a year. Compliancy Group and Abyde track both, and ExpiryEdge can remind each person directly.
Accountable is the only one here with prices on its site: $199, $299 or $799 a month, with a 7-day trial. You'll need a quote from Compliancy Group, Abyde, HIPAA One or Total Medical Compliance. ExpiryEdge plans run $29 to $199 a month and track the deadlines the program creates. The HHS SRA Tool is free to download.
Yes. ONC and HHS OCR publish the Security Risk Assessment Tool on HealthIT.gov, now at version 3.7, for small and medium providers. It walks you through the assessment. It won't track BAAs, training dates or OSHA, so you'll still need a system for those.
Six years. Under 45 CFR 164.316, you keep Security Rule policies and records for 6 years from the date they were created or last in effect, whichever is later. That covers risk analyses, policies and training logs, so store them where you can find them.
You do if they can access patient data while working for you. HHS treats any vendor that handles protected health information on your behalf as a business associate. Get it signed before they start. Compliancy Group, Abyde and ExpiryEdge can each collect e-signed BAAs, so you don't need paper.
Not medical, clinical, or HIPAA compliance advice
This article is for general informational purposes and does not constitute clinical or HIPAA compliance advice. ExpiryEdge is not currently a HIPAA Business Associate. Healthcare organisations handling Protected Health Information should review the specifics of their compliance programme with a qualified privacy officer or HIPAA consultant.