Compliance Solutions: How to Compare Tools Without Getting Burned
To compare compliance tools without regret, decide first which problem you're solving (missed deadlines, missing controls, or a programme you don't know how to build), then test each vendor live against your own scenarios rather than their demo script. Most bad purchases come from buying the wrong category of tool, not the wrong brand.
Getting burned usually looks like one of these:
- Deadlines still live in inboxes and spreadsheets because the tool is too heavy for daily use.
- Alerts fire, but nobody knows who owns the next step or what done means.
- Proof is scattered, so every audit turns into a scramble.
- You're paying for an enterprise platform when what you needed was renewal control.
This guide gives you a way to compare that's practical and hard to game in a demo.
Step 1: name the problem before you look at products
Most teams shop for "compliance software" when they really need one of three things.
Deadline control: renewals, licences, certificates, filings
If your biggest risk is something expiring unnoticed (a contractor's insurance certificate lapsing mid-job, a food hygiene certificate, a 60-day notice window on a SaaS contract), you need a register of what's due and when, a named owner with escalation, repeatable checklists, and the proof attached to each item.
Policy, risk and controls management
If your risk is that controls aren't defined, risks aren't assessed or policies go stale, you may need a broader governance, risk and compliance (GRC) platform.
Building a programme from scratch
If you're setting up something like a privacy programme (data mapping, impact assessments, training), software alone won't do it. You'll likely need specialist advice alongside it, especially if nobody in-house has done it before.
Deadline tools are quick to adopt and very hands-on. GRC suites do more but take longer to roll out. Teams get burned when they buy a GRC suite to fix missed renewals, or buy a renewal tracker and expect it to run their risk register.
Step 2: turn your must-haves into pass or fail tests
Don't list features. Write tests you can run during each demo. For example:
- "We can create a new licence record in under 60 seconds, with owner, renewal date, reminder schedule and an attached file."
- "If the owner hasn't finished the renewal checklist by the renew-by date, the system escalates to the backup and then to their manager."
- "For an audit, we can pull every obligation for our Leeds site, filter to overdue, and export the proof in a few minutes."
Now you're scoring what the tool does, not how good the presenter is.
Step 3: compare categories honestly
| Tool type | Best for | How you get burned | Check before buying |
|---|---|---|---|
| Spreadsheet and calendar | Very small scope, low stakes | Silent failures, version clashes, no audit trail | A named owner, a review routine, cover for holidays |
| General task or project tool | Simple task lists | Dates exist, but no proof or escalation per obligation | Can you tie files and approvals to each obligation? |
| Deadline-first compliance tool | Renewals, expiries, recurring obligations | Missing an integration or category you needed | Import and export, reminders, workflow, files, permissions |
| Full GRC suite | Risk registers, controls, policies and audits across the organisation | Slow rollout, low adoption, heavy admin | Time to first value, setup effort, real use by operators |
| Consultant-led programme | When you need expertise and change management | Reliance on outsiders with no internal routine | Deliverables, handover plan, who runs it afterwards |
If your daily pain is "we keep missing renewals", look at deadline-first tools before a full GRC suite. Our ExpiryEdge vs spreadsheets page shows where a spreadsheet stops being enough.
Step 4: use a scorecard that makes vendors show, not tell
Ask every vendor to do each of these live, with you watching:
| Area | What good looks like | Ask them to show you |
|---|---|---|
| Register | One place for obligations, dates, owners and status | Create a new obligation from scratch with the required fields |
| Reminders | Several reminders, configurable lead times, escalation | A 90, 60, 30 and 7 day schedule and the escalation path |
| Checklists | Repeatable steps with clear completion rules | A renewal checklist, and what happens when a step is skipped |
| Proof | Files attached to each obligation | Attach a document and show it in the audit view or export |
| Search | Find anything by site, category, owner or date | Filter everything for one site and export the list |
| Permissions | Role-based access and controlled edits | What a viewer can do compared with an editor |
| Import and export | Bulk import and a full export, so you're not locked in | Import 50 records, then export everything with metadata |
| Reporting | Overdue, upcoming and done, by owner, category or site | Renewals due in the next 60 days and who owns them |
| Setup effort | A pilot you can run without consultants | What week 1 looks like with our data |
If a vendor can't walk through these live, expect it to be worse after you've paid.
Step 5: price in the hidden costs
The licence fee is rarely what hurts. The real costs are admin time, rework and the compliance gaps a poor fit leaves open.
Configuration debt
A tool that needs heavy customisation creates a permanent admin backlog. Ask who'll maintain categories, templates and reminder rules, how changes get approved, and what happens when you open a new site.
Alert fatigue
If people learn to ignore reminders, the system has failed even though it's technically working. Check for reminders staged by urgency, owner and backup assignment, and escalation rules people can predict.
For reminder timing in detail, see our guide to expiration reminder setup timing.
Missing proof
Plenty of tools track tasks but not evidence, and in an audit "we did it" isn't enough. Ask how files attach to each obligation (not just to a project), whether uploads are timestamped, and how fast you can retrieve and export them under pressure.
Lock-in
If you can't export cleanly, you don't really own your register. At minimum you should get every obligation with its metadata, plus the attachments or a usable index of them.
No clear owner
If ownership is vague, you'll drift back to whoever happens to remember. Confirm that every obligation can carry a primary owner, a backup and an escalation contact.
Step 6: run a pilot with awkward cases, not the happy path
Keep it small, time-boxed and real. Two to four weeks is enough for reminders to fire and people to respond.
What to load
Pick 15 to 30 real obligations across different risk levels, and make sure the awkward cases are in there:
- A high-stakes renewal with a notice period, so the renew-by logic gets tested.
- A renewal with several steps and an approval.
- A site-specific requirement, to test filtering.
- At least one item that needs a document attached and later retrieved.
What to measure
Time to create a record. Whether owners knew what to do from the reminder alone. How many items closed without anyone chasing. And how long it took to produce a full audit packet for one obligation.
For a wider feature list to use alongside the pilot, see the compliance management software core features checklist.
Quick guide: which way to go
| If your situation is | Prioritise a tool that is strong in |
|---|---|
| Missed renewals and expiries are the main pain | Deadline tracking, escalation, checklists, attached proof |
| Audits hurt because proof is scattered | File attachment, search, export, permissions |
| Many sites, entities or franchises | Organising by location, bulk import, standard categories |
| You need organisation-wide risk and controls management | A GRC platform, plus a change management plan |
Where ExpiryEdge fits
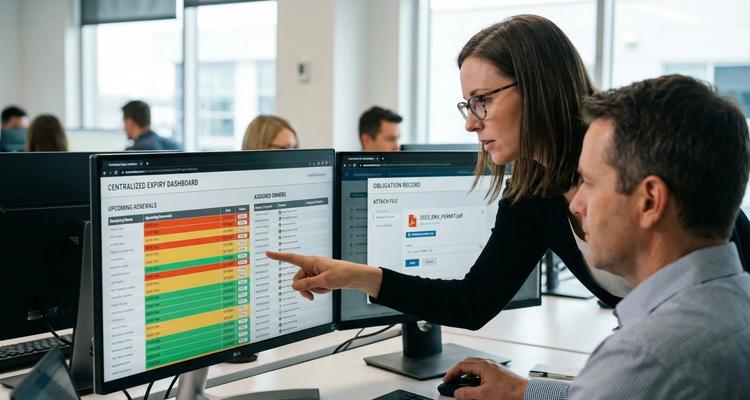
ExpiryEdge is a deadline-first tool. It tracks contract, licence, permit and certificate dates, reminds the owner by email, SMS, WhatsApp, Slack or Teams, escalates overdue items to a manager, requests and collects the renewed document, and keeps an exportable audit trail. It isn't a GRC suite: it won't run your risk register or policy library.
If deadlines are your problem, put it through the same pilot and scorecard as any other vendor, and measure time to completion and time to produce proof.
FAQ
What are compliance solutions in a business context?
Anything that helps you keep the promises the law, your contracts and your own policies make on your behalf. Some tools just track renewal dates. Others, often called GRC suites, run risk registers and policy libraries for the whole company. Then there are consultants, who build the programme with you. Most small teams need one of these first.
How do I compare compliance software without getting overwhelmed by features?
Ignore the feature grid. Write five or six pass or fail tests based on your real work, such as creating a licence record with an owner and reminder schedule, then escalating it when the owner misses the date. Ask every vendor to run the same tests live. Score what they actually do, not what the slide says.
What is the biggest red flag during a compliance software demo?
A vendor that shows polished dashboards but can't run your scenario live. If they won't create a record from scratch, trigger an escalation, attach a document and export it while you watch, assume it'll be harder after you've signed. Ask for a trial account with your own data before you commit.
Do we need a full GRC suite if we mainly struggle with renewals and deadlines?
Probably not. If your main pain is missed expiries and scattered proof, a deadline-first tool is usually quicker to roll out and easier for operators to adopt. GRC suites earn their cost when you need risk registers, control libraries and policy management across the whole organisation. Buy for the problem you have now.
How long should a pilot take for a compliance tool?
Two to four weeks is enough. That's long enough for real reminders to fire and owners to respond, and short enough that people stay focused. Load 15 to 30 real obligations across different risk levels, then measure how many closed without anyone chasing and how long one audit packet takes to produce.
What should we require for audit readiness?
One register for every obligation, a named owner on each, a repeatable checklist, the proof attached to the item it supports, and filters that let you pull everything for one site or category in minutes. Add a clean export of records and attachments, so you're never locked in when you change tools.
Run the pilot on your own data
Write your three pass or fail tests this week, then load 15 real obligations into each tool you're considering. ExpiryEdge has a 14-day free trial with no credit card, or you can book a walkthrough. See compliance management for how teams usually set it up.
Frequently asked questions
Ignore the feature grid. Write five or six pass or fail tests based on your real work, such as creating a licence record with an owner and reminder schedule, then escalating it when the owner misses the date. Ask every vendor to run the same tests live. Score what they actually do, not what the slide says.
A vendor that shows polished dashboards but can't run your scenario live. If they won't create a record from scratch, trigger an escalation, attach a document and export it while you watch, assume it'll be harder after you've signed. Ask for a trial account with your own data before you commit.
Probably not. If your main pain is missed expiries and scattered proof, a deadline-first tool is usually quicker to roll out and easier for operators to adopt. GRC suites earn their cost when you need risk registers, control libraries and policy management across the whole organisation. Buy for the problem you have now.
Two to four weeks is enough. That's long enough for real reminders to fire and owners to respond, and short enough that people stay focused. Load 15 to 30 real obligations across different risk levels, then measure how many closed without anyone chasing and how long one audit packet takes to produce.
One register for every obligation, a named owner on each, a repeatable checklist, the proof attached to the item it supports, and filters that let you pull everything for one site or category in minutes. Add a clean export of records and attachments, so you're never locked in when you change tools.